What is a cloud access security broker (CASB)?
Introduction
A Cloud Access Security Broker (CASB) is a security technology that helps organisations monitor and control activity within cloud applications. It provides visibility into how cloud services are being used, applies policies to protect sensitive data, detects suspicious or risky behaviour, and supports compliance across cloud environments.
CASB emerged as organisations moved business applications and data into SaaS platforms such as productivity suites, collaboration tools, cloud storage services, and CRM systems. Traditional security controls were designed to protect the corporate network, but they offered limited visibility into what users were doing inside cloud applications. CASB addresses that challenge by extending visibility, data protection, threat detection, and policy enforcement into cloud environments.
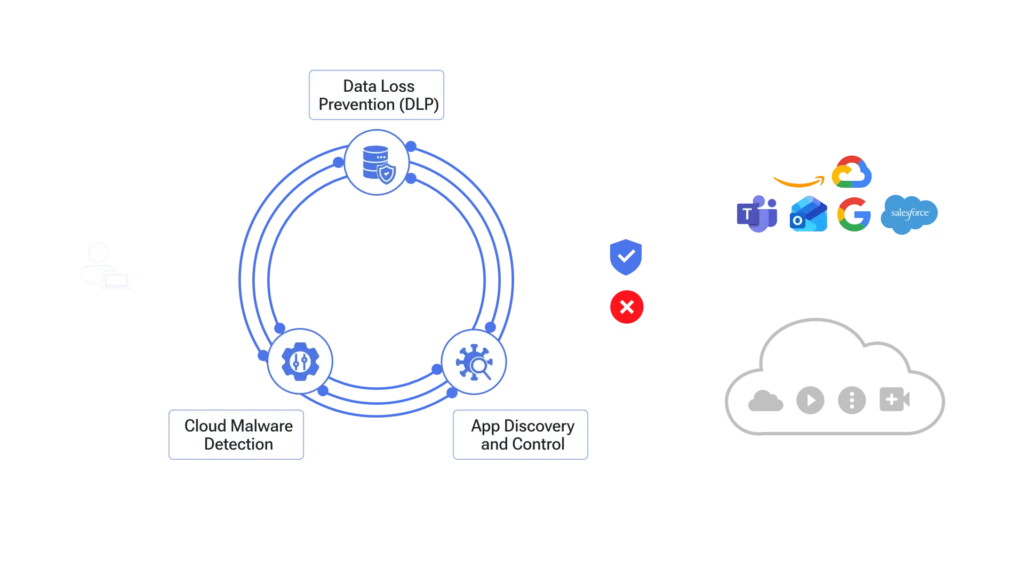
Why organisations deploy CASB?
Most deployments begin with a visibility problem the security team did not fully appreciate until CASB surfaced it. The IT team has a list of approved applications. The actual number of cloud services in active use is usually higher than expected and none of it appears in the security console because none of it passes through tools built to monitor the corporate network.
This is why most CASB deployments start in discovery mode. Visibility comes before enforcement because security teams need to understand actual user behaviour before introducing restrictive policies.
The most common triggers:
- Unapproved application usage — teams adopting file sharing tools, personal cloud storage, and collaboration platforms that never went through a security review
- Unmanaged devices — contractors, partners, and personal devices accessing cloud applications outside any security control
- Third-party access gaps — external users with broader cloud permissions than intended
- Compliance pressure — audit requirements that demand evidence of control over data in cloud environments the security team cannot currently see.
- Data exposure risk — sensitive files being shared, downloaded, or stored in ways that violate policy without anyone knowing
Organisations consistently find more exposure than they expected. That discovery is usually what drives the move from visibility into active enforcement.
The four core capabilities of CASB
- Visibility - Most organisations have more cloud applications in use than they realise. CASB helps uncover those applications and provides visibility into who is using them, from where, and on which devices. For many security teams, this is the first accurate view of their cloud application estate and the risks associated with it.
- Data security - Sensitive data continues to move long after it reaches a cloud application. CASB helps organisations control how files are shared, downloaded, and stored across SaaS platforms. It extends Data Loss Prevention (DLP) policies into cloud environments and allows the same security controls to be applied consistently across multiple applications. In practice, policy tuning is usually required to reduce false positives and align controls with how the business actually works.
- Threat protection - Many cloud security incidents involve legitimate user accounts rather than obvious attacks. CASB helps identify activity that falls outside normal behaviour, such as unusual login locations, unexpected download activity, or access patterns that do not match a user's typical behaviour. Many CASB platforms can also detect malicious files and suspicious activity within cloud applications, helping security teams investigate and respond before threats spread further.
- Compliance - As sensitive data moves into cloud applications, organisations still need to meet regulatory and audit requirements. CASB helps enforce security policies, maintain activity records, and provide the visibility needed to demonstrate compliance with frameworks such as GDPR, HIPAA, and PCI DSS.
Understand how CASB secures cloud applications
in real enterprise environments
How CASB works?
CASB operates across three sequential stages.
- Discovery CASB identifies cloud applications in use across the organisation within its monitoring scope: both sanctioned and unsanctioned. The goal is an accurate picture of the environment before any enforcement begins. Most organisations find more exposure here than expected.
- Classification CASB assesses each application for risk level, compliance posture, and data handling behaviour, and categorises data by type and sensitivity. Classification turns visibility into actionable intelligence, determining which applications to sanction, restrict, or block and what policies apply where.
- Remediation CASB applies policy actions continuously: allowing or blocking access, enforcing DLP policies, flagging and where platform permissions allow quarantining malicious files, and restricting specific actions such as uploads, downloads, or external sharing. As the environment changes, enforcement updates accordingly.
How is CASB implemented?
CASB reaches cloud applications through two deployment approaches. The strongest implementations use both.
- API mode: CASB connects to cloud platforms through their published APIs, scanning content already stored there. It covers data uploaded before deployment and extends to unmanaged devices, contractors, and partners who cannot be directed through a proxy.
- Inline mode: CASB sits in the traffic path, inspecting and enforcing policy in real time. It operates through two proxy models:
- Forward proxy: User traffic is routed through the CASB enforcement point before reaching the cloud application. Requires an agent or network-level traffic steering. Standard for managed corporate devices.
- Reverse proxy: CASB sits in front of the cloud application. Users are redirected through a CASB-controlled access point with no agent or device configuration required. Suited to BYOD, unmanaged devices, and third-party access.
API handles what is already in the cloud and what cannot be proxied. Inline handles real-time enforcement. A CASB supporting only one approach leaves gaps that will surface in practice.
CASB Use Cases
Organisations adopt CASB to solve a range of cloud security challenges that traditional network controls cannot fully address. From discovering unapproved applications to protect sensitive data and supporting compliance requirements, CASB provides the visibility and control needed to govern cloud application usage at scale.
- Discovers cloud applications in use across monitored traffic and connected environments, including unapproved ones
- Applies Data Loss Prevention (DLP) policies inside SaaS platforms
- Detects anomalous user behaviour and compromised accounts
- Helps identify malicious files and suspicious activity within cloud applications
- Enforces consistent policy across managed and unmanaged devices
- Controls uploads, downloads, sharing, and access at a granular level
- Provides audit trails for compliance across cloud environments
- Core component within SSE and complete SASE architectures
CASB within SSE and SASE
Organisations rarely deploy CASB in isolation. It is most commonly adopted as one of four components within a Security Service Edge (SSE) framework, alongside ZTNA, SWG, and FWaaS, or as part of the security enforcement layer within a complete SASE architecture. Explore our comprehensive SASE Guide to understand how these technologies work together to deliver secure, scalable connectivity.
Within a unified platform, CASB shares policy context with the other components. The identity ZTNA verified, the device posture it assessed, the access decision it made: all of it informs how CASB governs what that user does inside a cloud application. This is what makes CASB more effective as part of an integrated architecture than as a standalone tool.
CASB vs Related Technologies
| SASE Components | What it does | How it differs from CASB |
|---|---|---|
| SWG | Inspects and filters internet-bound traffic at the connection level | SWG handles the traffic layer. CASB handles what happens inside the application once the connection is established. Both run together in a properly configured SSE deployment. |
| ZTNA | Controls whether a user gets access to an application based on identity, device, and context | ZTNA is the access decision. CASB governs what the user does after access is granted: what data they touch, how they use it, whether their behaviour looks normal. |
| FWaaS | Controls traffic based on network-level attributes: source, destination, port, protocol | Firewalls have no visibility into application-layer activity. A user downloading an unusual volume of records from a cloud CRM does not trigger a firewall alert. CASB sees it. |
What to look for when evaluating CASB
Dual-mode operation: Ask whether the solution supports both inline and API modes. If not, ask specifically what gets missed.
SaaS application coverage: Match the provider's supported application library against what your organisation actually uses. The applications that create the most risk in your environment may not be the most common ones on a generic list.
DLP policy depth: Generic classification catches obvious cases. Ask what the capability covers for your specific compliance requirements and data types, not for a feature name on a checklist.
Identity integration: Verify the integration covers all user populations: employees, contractors, partners, and unmanaged device users. Partial integration produces partial visibility.
Platform integration: A CASB requiring separate policy management from the rest of your security stack recreates the fragmentation you are trying to eliminate.
Organisations adopting SSE often find that separate policy engines create unnecessary operational complexity and administration overhead.
Need to evaluate SASE for your environment?
Discuss your current network, cloud access, and security setup to identify where
Orixcom SASE can simplify operations and improve control.
How Orixcom delivers CASB
We deliver CASB as part of our fully managed SSE and SASE services, underpinned by Cisco Umbrella technology. As a Cisco Trusted MSSP, we integrate CASB into a unified security framework alongside ZTNA, SWG, and FWaaS, ensuring policies, visibility, and access context are consistent across the entire environment, not fragmented across tools.
For organisations where CASB is the starting point, we begin with discovery. This phase consistently uncovers more cloud usage and risk than expected. From there, we build policies based on real-world activity, not assumptions, giving you immediate, actionable control over your SaaS environment.