Connectivity
Connecting users,
locations, applications & workloads
Carrier-grade enterprise connectivity solutions that unify usrrs, sites, data centres, clouds, and applications, seamlessly and at scale.
Need help mapping your network journey?
Platform
The Orixcom Platform
Explore an enterprise ready portfolio of products built to support complex business goals and long-term growth.
Need help mapping your Connectivity journey?
SASE
Secure users, devices and
workloads, anytime, anywhere.
Explore an enterprise ready portfolio of products built to support complex business goals and long-term growth.
Need help mapping your SASE journey?
Company
Need more
information?
Our team is always here
to help you, just reach
out anytime.
Support
Secure Access Service Edge (SASE): A comprehensive guide for enterprises & growing businesses
Introduction
Most organisations are running a network designed for an office that no longer exists. SASE (Secure Access Service Edge) converges networking and security into a cloud-delivered framework that applies consistent policy across users, locations, cloud environments and applications. Today, users connect from home, hotels and co-working spaces. Applications sit across SaaS, AWS, Azure and data centres simultaneously. Traffic no longer follows a predictable path, and yet most organisations are still applying security as though it does. The result is not just a security gap; it is an operational one.
Network teams manage connectivity tools, security teams manage access and threat controls, and the two often have fragmented visibility across the environment. When something breaks, or worse, when something is breached, the investigation spans multiple tools, vendors and teams.
This guide explains what SASE is, how it works, what it requires, and how to evaluate whether it is the right direction for your organisation, whether you are a large enterprise managing infrastructure across regions or a growing business building a secure foundation without overcomplicating it.
Understand how Orixcom SASE fits
your network architecture
Traditional security models are no longer enough
Most organisations did not arrive at their current architecture through a single bad decision. They arrived through a sequence of reasonable ones; each made in response to a specific problem at a specific point in time. The difficulty is that those decisions were made for environments that no longer exist.
Applications are in multiple clouds
Users are everywhere
Perimeter is dissolved
Security tools are siloed & complex
The enterprise problem: Scale without consistency
The problem isn't only the number of tools, it's that none of them share a common view of the environment or enforce policy consistently across it.
Security policies break down beyond HQ
As users, applications, and locations expand, consistent policies become difficult to maintain.
Access controls don't align across departments
The same user may often have different security controls across VPN, SaaS and cloud apps.
Cloud visibility gaps
Cloud and on-prem traffic frequently bypass legacy security controls.
Investigations span across tools
IT teams spend more time finding data from different tools, delaying resolution and increasing costs.
The growing business problem: Speed without structure
Growing businesses often prioritise near-term needs, adding tools that solve immediate problems but create complexity over time as the environment grows.
VPN becomes the
bottleneck
VPN worked for office-first environments. Remote work and SaaS adoption exposed its limitations.
IT runs platforms instead of policy
Small or lack of IT teams spend more time managing tools than improving security and governance.
Reactive tools don't form an architecture
Individual tools solve immediate needs but create fragmented visibility and control.
Cost implications
Deliberate architecture decisions today help avoid the future cost of technical debt.
How SASE Works: Architecture, Components, Traffic Flow and PoP Role
The core components of SASE and how they work together
SASE combines five core capabilities, under a shared policy framework:
- SD-WAN — Routes traffic across available links based on application need, not fixed paths.
- ZTNA — Replaces broad network access with application-level access, verified by identity and device posture.
- SWG — Inspects internet-bound traffic against policy at the nearest cloud point, not at a central choke point.
- CASB — Gives visibility and control over SaaS use, including data that on-premises tools cannot reach.
- FWaaS — Delivers firewall enforcement from the cloud, across users and locations, without physical appliances.
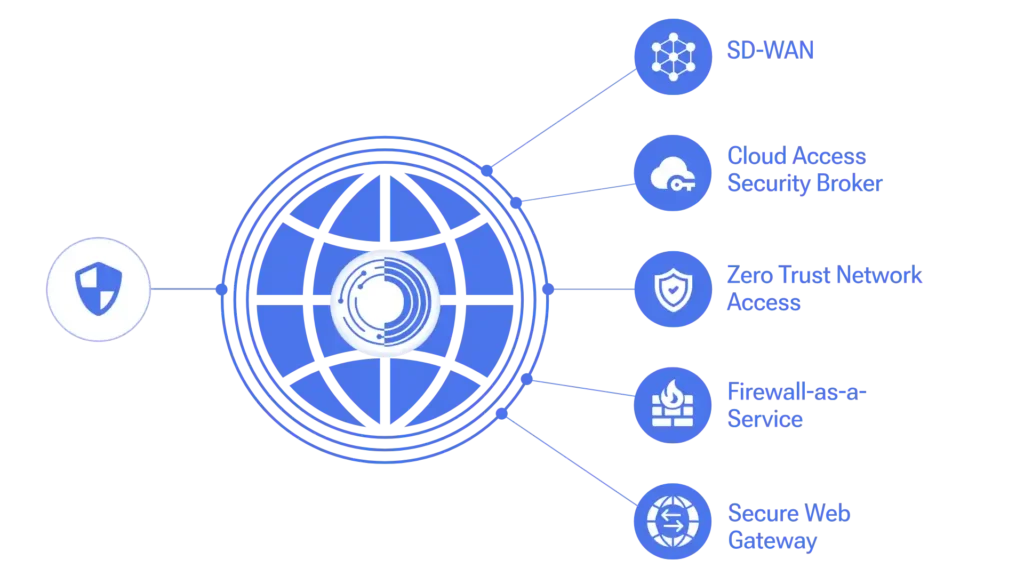
The policy layer is what turns individual capabilities into a SASE architecture. A single framework applies policies consistently across all enforcement points.
SASE architecture: What the structure actually means
SASE architecture operates across three layers. They work together, not independently, and the way they share a single policy framework is what separates a SASE deployment from a collection of integrated tools.
The connectivity layer is where SD-WAN sits and handles how traffic moves between users, branches, cloud environments and data centres.
The enforcement layer is where ZTNA, SWG, CASB and FWaaS operate, applying security controls at the PoP closest to the user.
The policy layer is the element most often underestimated. It looks like configuration sitting above the other two layers, but it is the architectural element that makes them coherent: one framework that governs how connectivity and enforcement behave across every environment simultaneously. Without it, the components below are tools running in parallel, not an architecture.
How Traffic Flows Through a SASE Environment
Traditional security relies on fixed inspection points. When users work remotely or applications move to the cloud, traffic often bypasses those controls.
SASE takes a different approach. Security is applied at the cloud enforcement point closest to the user, before traffic reaches its destination.
- Users connect from any location.
- Traffic is directed to the nearest SASE PoP.
- Identity and device posture are verified.
- Security policies are applied.
- Access is allowed or denied based on policy.
- SD‑WAN can optimise routing where deployed.
Security enforcement travels with the user rather than waiting at a fixed perimeter. Access is verified and protected at the cloud enforcement point closest to the user.
The Role of Points of Presence
Points of Presence (PoPs) are the distributed cloud locations through which a SASE provider delivers traffic inspection, access control, and routing. Their coverage matters for two reasons that directly affect business outcomes.
Policy consistency: If users in certain locations are distant from the nearest PoP, enforcement gaps emerge. Consistent security requires consistent enforcement infrastructure, wherever your users are. Evaluating PoP coverage against your actual user distribution, not a provider's global marketing map, is a practical necessity.
Performance: Traffic that must travel far to reach an enforcement point before its destination introduces latency. A provider with limited PoP coverage may enforce policy consistently in theory but deliver poor application performance in practice.
Simplified inventory management
Keep track of stock, streamline supply chains, and optimize inventory levels with ease.

SASE Use Cases: What it looks like in real environments
Consistent security across distributed environments
Challenge: Security policies are interpreted differently across sites, clouds, users, and regions, creating inconsistent access control, fragmented visibility and higher governance risk.
Solution: A SASE deployment centralises policy across every user, location and cloud environment, so access rules are applied consistently from every enforcement point.
Impact
Enterprises gain stronger governance, simpler policy management and consistent protection across distributed operations.
Protecting hybrid workforces wherever they connect
Challenge: Concentrating security at a fixed network edge fails when most users connect from outside it. Backhauling remote traffic for inspection adds latency without improving protection.
Solution: SASE applies identity-based access, device posture checks, secure web gateway inspection, SaaS visibility and cloud firewall enforcement through cloud points of presence closer to the user.
Impact
Consistent access, stronger protection and better application performance from any location.
From VPN dependency to zero trust network access
Challenge: VPN grants users access to the network, not just the application they need. As hybrid teams grow, this creates unnecessary exposure, increases operational overhead and makes access harder to manage securely.
Solution: ZTNA replaces VPN with verified, application-level access based on identity, device posture and policy. For growing businesses without a complex WAN, SSE addresses the core security gap without requiring a full network redesign.
Impact
Businesses reduce unnecessary network exposure, simplify remote access management and create a more scalable foundation for secure growth.
Regaining complete control over SaaS and Shadow IT
Challenge: Sensitive data now lives across SaaS apps that on-premises tools cannot inspect. Shadow IT is unknown, unmanaged access and risky data movement often remain hidden.
Solution: A SASE improves SaaS visibility, CASB controls, data protection policies, secure web gateway inspection and cloud-based enforcement together, so organisations can govern sanctioned and unsanctioned app usage more consistently.
Impact
Enterprises gain stronger governance, simpler policy management and consistent protection across distributed operations.
Building a SASE strategy that fits your organisation
Organisations are hardly looking for SASE by name. They are trying to solve practical problems: VPN access that is hard to manage, SaaS usage they cannot fully see, inconsistent policies across locations, rising tool costs or poor application experience for remote users.
The right starting point is not “which SASE platform do we buy?” It is “which gap is creating the most cost, operational or security risk today?” A meaningful assessment focuses on three gaps where SASE delivers the highest return:
Access gap
Gain visibility and control over SaaS applications and user activity.
Visibility gap
Where SaaS use is uninspected.
Where shadow IT is unknown.
Where cloud workloads fall outside existing security controls.
Where internet-bound traffic bypasses inspection.
Policy gap
Where access rules differ across HQ, branches, remote users, and multicloud.
Where policy changes need to be repeated across multiple tools.
Where teams cannot easily prove what is being enforced at what location.
Where enterprises should begin
For most enterprises, the remote access layer is the logical starting point. Replacing VPN with ZTNA closes a major security gap without requiring changes to the underlying WAN. It is one of the fastest ways to align security with how the workforce operates today.
Start with ZTNA
Migrate user groups and applications in controlled phases. Validate each phase before moving the next group across.
Extend visibility with SWG and CASB
Close the SaaS and internet visibility gaps that perimeter-era controls were never designed to reach.
Add FWaaS
Consolidate firewall enforcement under the same policy framework rather than running it as a separate stack.
Align connectivity
Bring SD-WAN into the SASE policy framework when branch performance, connectivity reliability or operational cost justifies it.
Where growing business should begin
Growing businesses rarely need to begin with a full SASE deployment. The practical approach is to address the most immediate risk first, establish a scalable security foundation, and then expand capabilities as the business grows and requirements evolve:
Replace VPN with ZTNA
ZTNA is the immediate priority. Supplement VPN to reduce access risk, support remote work and apply more granular access controls.
Improve visibility with SWG & CASB
Improve visibility, control shadow IT, secure internet traffic and strengthen SaaS governance.
Reduce WAN complexity
SSE covers the core security requirements without adding unnecessary WAN complexity. Add SD‑WAN later as the business grows.
Improve branch performance
SD‑WAN with SASE-aligned security improves connectivity, performance and resilience under a shared policy framework.
A short supporting check on compliance obligations (traffic inspection, data residency, access event logging) and internal capacity (whether the team can run SASE or needs a managed service from day one) rounds the assessment out.
This assessment does not need to be exhaustive before progress begins, but its outputs should determine what gets deployed and when, not the reverse.
What slows down SASE adoption
Most SASE deployments that underdeliver do so for one of three reasons. None of them are technology failures.
- Undefined policy: Tools are deployed before access rules are defined. Without clarity on who should access what, from which device and under what conditions, SASE cannot enforce meaningful control.
- Limited or siloed IT capacity: Networking and security may sit in separate teams, or with a small IT team already stretched across daily operations. Without clear ownership for policy, monitoring and incident response, SASE can become another platform to manage instead of a simpler operating model.
- Rushed migration: VPN, firewall or WAN changes are treated as a cutover instead of a phased transition. This increases disruption risk and can reduce confidence before the new model has stabilised.
Not sure where your organisation sits?
Every environment is different. If you are uncertain which components apply
to your current infrastructure, or you want an independent view of where your
most significant security and connectivity gaps are, Orixcom can assess your
environment and provide a clear recommendation, without a predetermined solution in mind.
How Orixcom supports your SASE journey
Orixcom delivers SASE as a managed service that brings connectivity, security, policy and operations into one coordinated model. Rather than deploying isolated tools, Orixcom designs the network and security layers together, so access, inspection, routing and support operate around the customer’s environment. Through trusted partnerships with leading platforms including Cisco and Cloudflare, Orixcom delivers the capabilities organisations need to modernise secure access, protect hybrid workforces, improve SaaS visibility and align connectivity with cloud security requirements.
SASE and SSE assessment
Map your current environment to identify the right starting point for access, visibility, policy and operational maturity.
Policy framework definition
Define how access, inspection and enforcement should work across users, devices, applications and locations.
Phased migration planning
Transition from VPN, legacy controls or fragmented tools seamlessly in stages to reduce disruption and validate progress.
Deployment and integration support
Coordinate implementation across identity, endpoint, security and network environments for a smoother rollout.
Policy lifecycle management
Review, refine and optimise policies as users, applications and business requirements change.
24x7x365 monitoring and support
Monitor, escalate and support incidents through defined SLAs and a single operational workflow.
Orixcom supports enterprises and growing businesses at different stages of SASE maturity, from organisations identifying their first secure access priority to those refining an existing deployment that needs stronger policy, visibility or operational ownership.
FAQs
How does SASE help enterprises reduce complexity across regions and clouds?
SASE centralises policy enforcement, visibility and access governance across distributed environments. This helps reduce operational fragmentation and improve consistency across regions, cloud platforms and remote users.
How important are Points of Presence (PoPs)?
PoP coverage affects both performance and policy enforcement. Limited coverage can increase latency and create inconsistent user experiences. Organisations should assess PoP locations against where their users actually connect.
Single-vendor vs dual-vendor SASE: Which is better?
Single-vendor can simplify integration, policy management and support. Dual-vendor approaches may offer greater flexibility but often require more operational coordination. The right choice depends on existing infrastructure, internal expertise and long-term operating requirements.
Should SASE be managed internally or delivered as a managed service?
That depends on internal capability. Organisations with dedicated networking and security teams may manage SASE directly, while others may prefer a managed service model that provides monitoring, policy management and operational support.
What are the most common reasons SASE projects underperform?
SASE projects often struggle because of:
- Undefined access and security policies
- Limited operational ownership
- Siloed networking and security teams
- Rushed migrations from VPN or legacy environments
Successful deployments typically prioritise policy design and phased migration.
What KPIs should we track?
Useful SASE KPIs often include:
- Improved SaaS and internet visibility
- Faster incident response
- Reduced operational complexity
- Better remote-user experience
- More consistent policy enforcement
- Reduced security risk exposure
The right KPIs depend on the security, operational and connectivity objectives behind the deployment.
Plan your SASE journey with confidence.
Assess your current and prioritise the security and
networking capabilities that matter most.
Business Connectivity, Simplified.
Copyright © Orixcom | Legal | Terms & Conditions | Privacy Policy
The Orixcom Platform
Company
Insights & Resources
Office Information
Dublin, Ireland
+35312630050
Dubai, United Arab Emirates
+97144249100