Zero Trust Network Access (ZTNA)
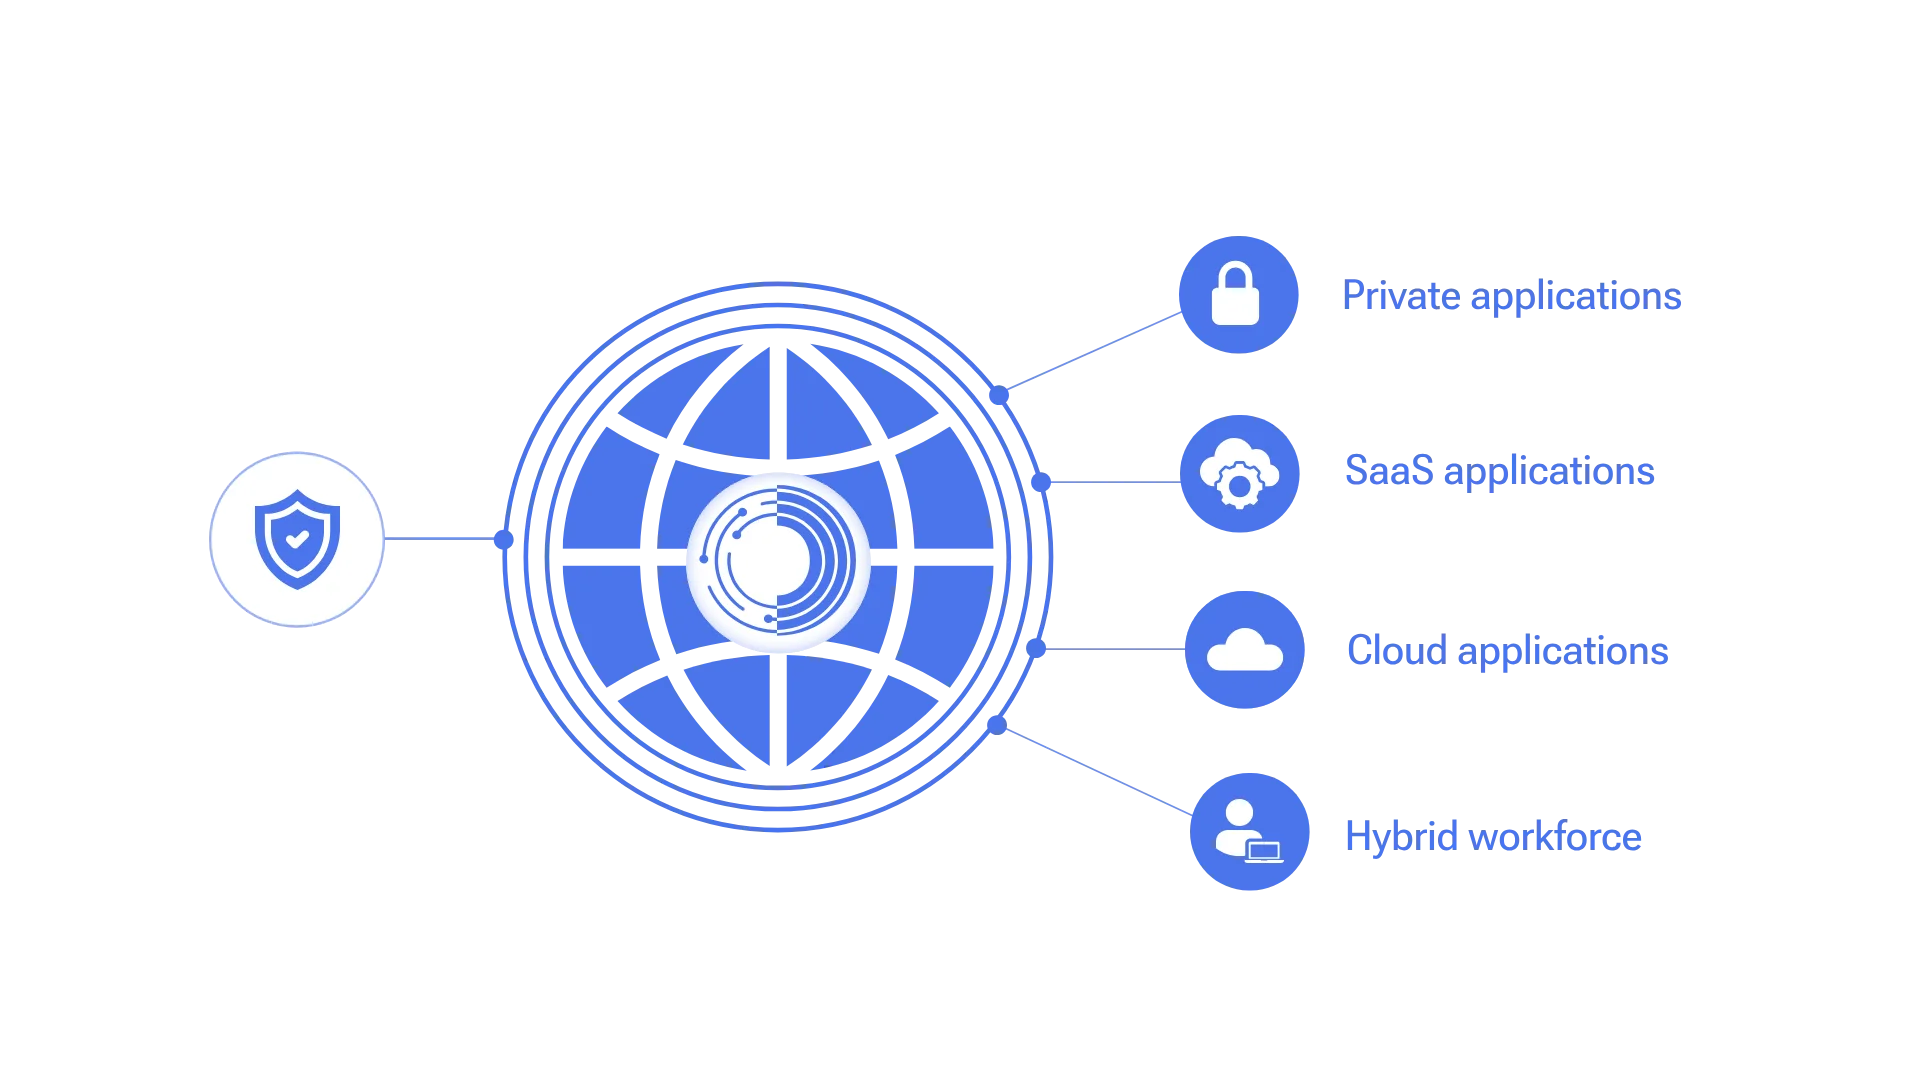
Zero Trust Network Access (ZTNA) secures all access across your applications and environment, from any user, device and location.
Benefits of Orixcom ZTNA
Establish user trust
Verify user identity with Duo MFA and Duo Push. Prevent credential-based attacks and ensure secure, seamless authentication.
Enforce adaptive access policies
Apply contextual policies based on user role, location, device type, and risk level. Grant least-privilege access to protect sensitive resources.
Secure access to all applications
Enable secure access to cloud and on-prem apps using trusted user and device validation. Strengthen your security posture across platforms.
Establish device trust
Assess device health during login to ensure only secure endpoints connect to your systems, regardless of user identity.
Gain visibility into user devices
Monitor device posture and software status to identify vulnerabilities. Ensure only compliant devices are granted access.
Unmatched value with Duo Security
Simplify ZTNA deployment with Duo’s integrated MFA, passwordless login, SSO, and self-service tools, reducing IT overhead.
Schedule a ZTNA demo
Talk to us to explore how Zero Trust can secure your workforce and simplify access management.
Secure your hybrid workforce with ZTNA
Zero Trust Network Access (ZTNA) delivers secure, identity-based access to applications, no matter where users are located. By verifying user identity and device health before granting access, ZTNA ensures only authorised users connect to the resources they need.
ZTNA also integrates seamlessly with Cisco Duo’s MFA solution, enabling fast, secure authentication via Duo Push. Combined with adaptive access policies and full visibility into user devices, it creates a resilient framework for secure remote work.
With ZTNA, implicit trust is eliminated. Access is granted based on context, such as user role, location, and device posture, reducing the risk of lateral movement and protecting sensitive data.
This approach strengthens your remote access strategy while minimising attack surfaces, ensuring that only trusted users and devices interact with your critical applications.
Discover more about
Orixcom ZTNA
Blog
Achieving zero trust with SD-WAN:
The foundation of a SASE-enabled architecture
Facts & Numbers
Glossary
Guide
The modern enterprise guide
to Orixcom SASE
Explore the architecture, advantages, and
implementation path for SASE.
Trusted by
Better together
Cisco Duo Security
Strengthen your device security with Cisco Duo’s multi-factor authentication (MFA)
Cisco Umbrella
Safeguard your organisation from cyberattacks with Cisco Umbrella
SASE
Revolutionise your network security and performance with the power of SASE
Your goals. Your bundle. Your way.
Share your business goals, and our experts will build the right combination for your business.
FAQs
Can’t find what you’re looking for?
What is Zero Trust Network Access (ZTNA)?
ZTNA is a security approach that assumes no user or device is trusted by default and grants access only to specific applications based on identity, device health, and context. It reduces the attack surface by avoiding broad network access and instead providing controlled, application‑level access.
How is ZTNA different from a traditional VPN?
A VPN typically gives users wide access to the internal network once connected, which can enable lateral movement if an account is compromised. ZTNA, by contrast, grants least‑privilege, app‑level access and continuously verifies user and device trust, significantly limiting exposure.
Is ZTNA only for remote workers?
ZTNA is ideal for remote and hybrid users but can also secure on‑site users accessing sensitive apps. Many organisations use ZTNA as a unified model for all access so policies are consistent regardless of location.
How does ZTNA improve user experience?
Modern ZTNA solutions can provide direct, optimised connections to applications rather than backhauling all traffic through a central data centre. This often leads to lower latency and simpler, SSO‑based access while maintaining strong security.
What security controls are typically part of ZTNA?
ZTNA commonly integrates identity and access management, device posture checks, micro‑segmentation, continuous monitoring, and centralised policy enforcement. These elements work together to implement least‑privilege access and detect abnormal behaviour in real time.
Can ZTNA protect both on‑premises and cloud applications?
Yes, ZTNA is designed to secure access to private data‑centre apps, IaaS workloads, and SaaS applications under a single policy framework. This unified model helps organisations move away from separate remote access tools for each environment.
What happens if a device becomes non‑compliant mid‑session?
ZTNA can continuously assess device posture and user behaviour and automatically revoke or downgrade access if risk levels change. Policies can force re‑authentication, trigger MFA, or terminate the session to prevent misuse.
How does ZTNA help with compliance and auditing?
ZTNA centralises logging of who accessed which application, from which device, and under what conditions. This level of detail supports compliance requirements around access control, auditing, and incident investigation.
Implement a zero trust strategy today
Enable secure, seamless access for all users, across any device, location, or application